
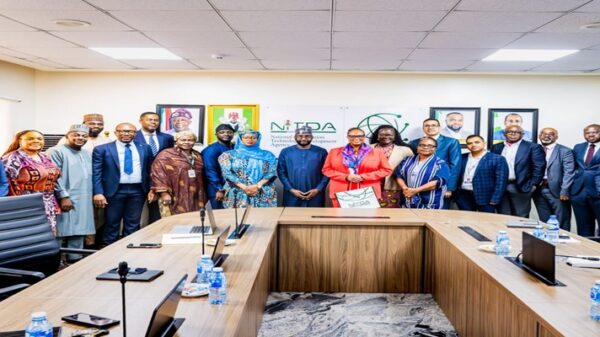










In a move to forestall cybersecurity risks in government-owned organisations, the National Information Technology Development Agency (NITDA) has mandated all Ministries, Departments and Agencies of government to implement of the DNS Security (DNSSEC) architecture, RaveNewsOnline reports.
The Agency says this will form part of its cybersecurity assessment protocol.
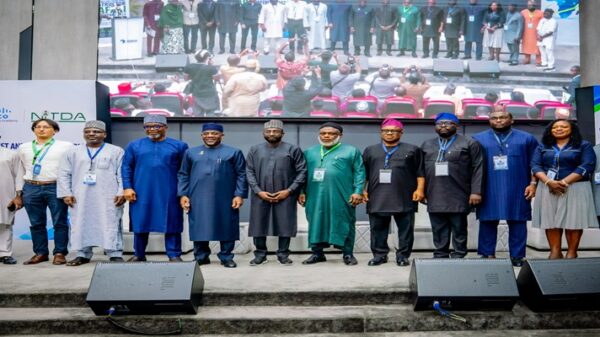
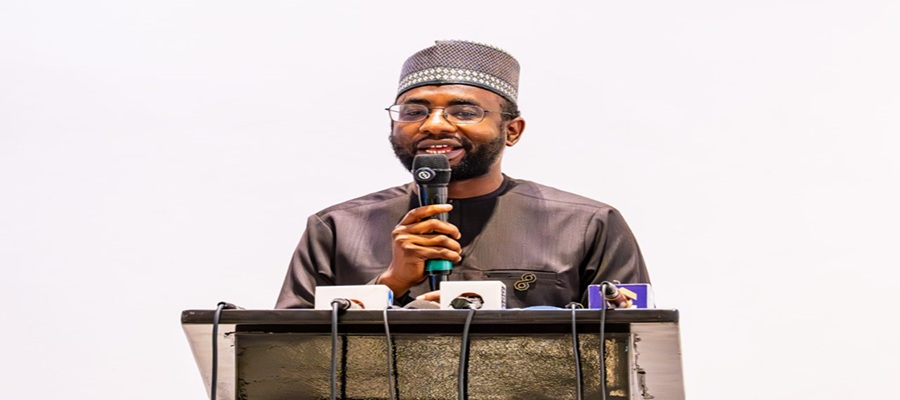
Speaking at the Cybersecurity Awareness Webinar held on Monday with its theme as “Securing Nigeria’s Digital Foundation: DNSSEC, the .ng Domain, and the Future of National Cyber Resilience”, the Director General of NITDA, Malam Kashifu Inuwa Abdullahi emphasized on the need to firmly implement DNS security as part of infrastructure architecture to will ensure the safety of domain names, and further give the Nigerian resource a global footing.
In his speech at the Webinar organized by the Nigeria Internet Registration Association (NiRA) through its .ng Academy; as part of events commemorating the Cybersecurity Awareness Month, the NITDA DG, represented by Mr. Oluwasegun Falayan, noted that DNSSEC is a necessity at the point the country is, and it is important for stakeholders to tackle issues that are related to DNSSEC as much as NITDA must also provide an avenue for DNSSEC to thrive. “Security goes beyond just the physical, but also our private space must also be secured.”
“So we must lead, we must ensure that every .gov.ng is signed as much as possible, and we provide DNS as an inclusion in every security assessment that we do. So it’s not enough to just have a domain, but it must be secured and must be signed.”
In his speech earlier, NiRA President, Mr. Adesola Akinsanya emphasized on the need to prioritise quality and security of domain names as against the number of domain names registered.
“There is also a critical consideration: where DNSSEC is improperly configured, domains can become inaccessible to users whose resolvers validate signatures.
“Our priority must therefore be competence, coordination and careful implementation, rather than adoption for its own sake,” he noted.
He explained DNSSEC in its simplest form. The Domain Name System (DNS) is often described as the internet’s phonebook, helping users find their way to websites and online services.
DNS Security Extensions (DNSSEC) add a layer of trust by using digital signatures that allow validating resolvers to verify that DNS responses are authentic and have not been tampered with.
“However, DNSSEC does not encrypt internet traffic, prevent traffic-flooding attacks, or protect against compromised registrar credentials.
“It is an important layer of security, but it must work alongside other protective measures to create a resilient digital ecosystem,” Akinsanya explained.
The NiRA President further referenced reports indicating increasing cyber breaches.
“Check Point reports that the average Nigerian organisation faced about 4,361 attempted attacks a week in June, against a global average of about 2,270.
“NIBSS reports digital-payment fraud of ₦25.85 billion in 2025, even as reported incidents fell, which NIBSS itself warns may signal under-reporting rather than safety. DNS security is not a technical hobby. It is an economic question.”
October is Cybersecurity Awareness Month, and the National Cybersecurity Alliance’s call this year is plain: “Don’t make it easy for them.” This morning is about the easy things: the unlocked, the unsigned and the unmonitored.
Further clarifying NiRA’s role, and the need for partnership, Mr. Akinsanya said: “NiRA runs the registry. We sign the zone, publish accurate data, support registrars and convene.
“We do not run your DNS, manage your registrar account, choose your provider’s resolver, or investigate crime. That is the case for partnership.”
He laid charges on various stakeholders. “Government bodies: review the domains you run. Who holds the login? Is multi-factor authentication on? Who is called at three in the morning when records change?
Regulators: make sure the naming layer is named in the forthcoming cybersecurity framework and in critical-infrastructure planning.
Internet providers: switch on validation and keep your resolvers patched.
Registrars: 15 of 164 is not a number I can defend.
Businesses: ask your provider whether your domain is signed and who can change your records.
Security professionals: share what you see and report incidents, because under-reporting is the enemy of everything we discuss today.”
The NiRA President explained that growth and trust must be the overarching goal, and no part of the 30% growth aim will be pursued at the expense of security. “But I am not asking for more domains for their own sake. A .ng that is unsafe or unreliable is worse than none.”
He encouraged registrars, internet service providers, government institutions, technical communities and other stakeholders to work together to expand DNSSEC adoption, strengthen implementation capacity and build greater trust in Nigeria’s digital infrastructure.
“Securing our digital foundation is a shared responsibility, and our collective commitment will determine how effectively we protect the future of the .ng namespace and Nigeria’s wider digital economy. A .ng name is more than an address.
“It is a statement of where you belong and who answers when something goes wrong. On the figures reported this year, .ng has roughly one domain for every thousand Nigerians; Kenya has about two and South Africa about twenty.”
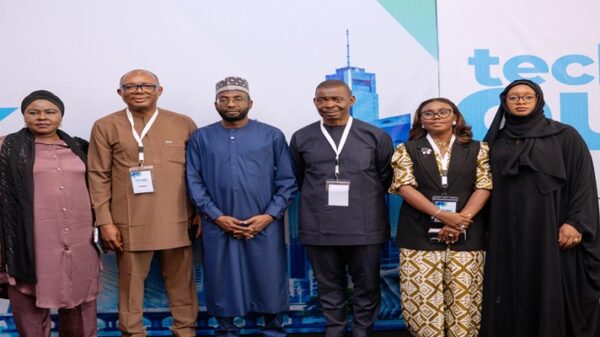
Speaking during a high-powered Panel Session, Head of Incident Handling at the Nigeria Computer Emergency Response Team (ngCERT), operating under the Office of the National Security Adviser (ONSA), Daniel Onyekpeze said cybersecurity incidences exist due to the growth rate of industrialization of social engineering with the use of AI, and data exposure.
Onyekpeze proposed an Executive Order giving DNSSEC a Critical National Information Infrastructure (CNII) status.
He said DNSSEC should be implemented across board, including in the financial sector. And it must be properly implemented.
IT and Cybersecurity Officer at the Nigeria Data Protection Commission (NDPC), Abubakar Mahmud who represented the NDPC National Commissioner/CEO Dr. Vincent Olatunji noted that large data can prompt data attacks.
Nigeria Police Force NCCC, SP Kuma Ikyereve disclosed that phishing tops the list of cybersecurity cases.
Founder and Chief Executive Officer (CEO) of CyberPlural, Lateef Hamzat said attacks are gradually moving away from targeting individuals to targeting systems.
Participants at the Webinar agree that Nigeria should take the implementation of DNSSEC seriously because securing the country’s cyber digital signature is more important than onboarding more domain names without security backing.
They therefore called on organisations to implement the free resource to keep their data safe.